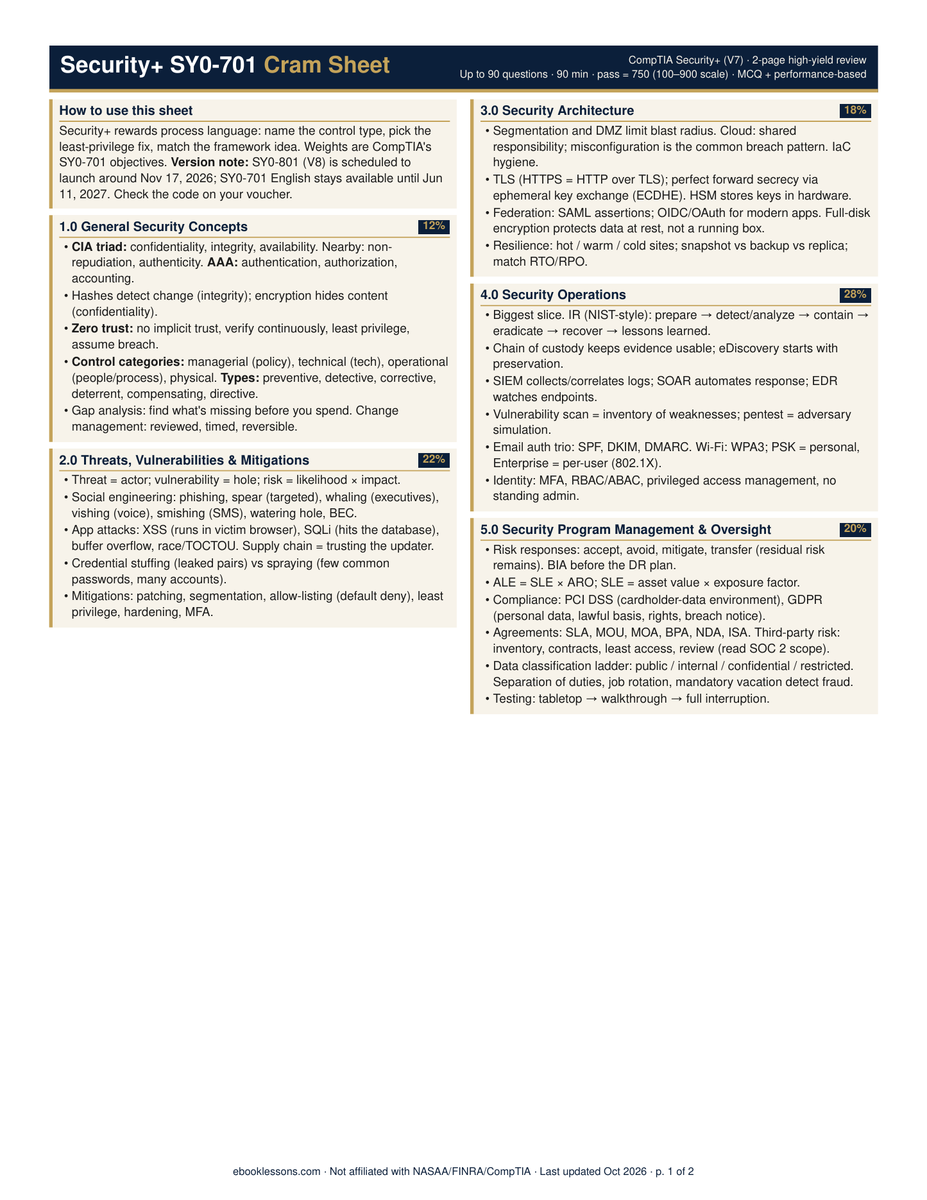
CompTIA Security+ SY0-701 Cram Sheet (2 pages)
Covers CompTIA Security+ SY0-701 · Written and maintained by Todd Lavergne, Todd Lavergne Media · Last updated Oct 2026
Security+ questions reward quick recognition: name the attack, pick the control type, choose the least-privilege fix. This two-page cram sheet is built for that last-week review.
Page 1 summarizes all five SY0-701 domains with CompTIA’s weights. Security Operations (28%) gets the most room: the incident-response steps, chain of custody, SIEM vs SOAR vs EDR, and scanning vs pentesting.
Page 2 has the charts:
- Attack types, with the warning sign and the best mitigation for each. It covers phishing, BEC, XSS, SQL injection, buffer overflow, credential stuffing vs spraying, ransomware, supply chain, watering hole and TOCTOU.
- A control category × control type grid, so “technical detective” or “managerial preventive” questions stop being guesswork.
- The common ports, paired with their services.
- Plain-English acronyms and the numbers to memorize: up to 90 questions, 90 minutes, 750 on a 100–900 scale, and ALE = SLE × ARO.
It’s drawn from our Security+ Complete Guide and CompTIA’s SY0-701 objectives. It’s a summary, not a full course. It pairs well with Professor Messer’s free videos or Jason Dion’s practice tests as a low-cost add-on.
Timing note: CompTIA plans to launch SY0-801 around November 17, 2026. SY0-701 stays available in English until June 11, 2027. This sheet covers SY0-701 only, so check the exam code on your voucher.
Letter-size PDF. Updated October 2026. Independent study aid; not affiliated with CompTIA.